Rig Security emerges from stealth with $12M to secure AI agents using human identities
 Daniel Levi
Posted On September 29, 2026

AI agents have an identity problem: they often don’t have their own identities. Instead, they operate through the credentials and sessions of humans and service accounts, making their actions difficult for traditional security tools to distinguish from those of the people behind them.
Rig Security thinks that blind spot is becoming a serious enterprise security problem.
The cybersecurity startup emerged from stealth Monday with $12 million in seed funding to build identity protection software that can identify AI agents operating through human and machine accounts and stop risky actions in real time.
Ten Eleven Ventures and Brightmind Partners co-led the round, joined by the CrowdStrike Falcon Fund and a group of cybersecurity founders and executives that includes Wiz co-founder and CTO Ami Luttwak.
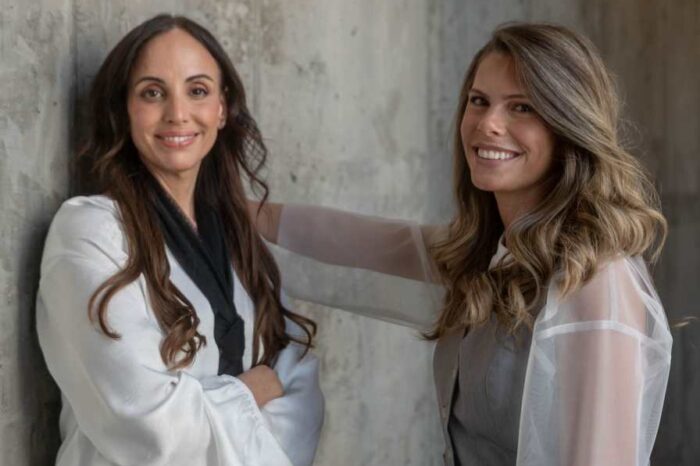
Rig was founded by CEO Guy Kozliner, a former member of Luttwak’s team at Wiz. The leadership team includes CTO Nokky Goren, the first engineer at Axis Security before its acquisition by HPE, and Head of Product Michal Haikov, who previously worked at Israel’s Unit 8200 and Flow Security, which CrowdStrike acquired.
The problem Rig is chasing comes from a basic mismatch between how enterprise identity systems were built and how AI agents work.
Companies spent years assigning permissions to employees, service accounts, and applications. AI coding assistants and autonomous agents can now operate through those existing accounts and sessions. From the perspective of an identity provider or security log, an action taken by an AI agent can appear to have been performed by the employee whose credentials it used.
That creates an uncomfortable question for security teams: when an account suddenly deletes data, changes infrastructure or accesses sensitive information, was it the employee or an AI agent acting on that employee’s behalf?
“Identity used to mean people’s credentials. Today, the most active identities in an enterprise are AI agents, and they are acting under human names,” Kozliner said. “Security teams can see that an account did something dangerous. What they cannot see is whether a person did it or an agent did, and they cannot stop the agent without blocking the person.”
Separating the AI agent from the human behind the account
Rig’s approach combines identity correlation with endpoint monitoring.
At the center of its platform is RICE, short for Rig Identity Correlation Engine. The company says the system uses machine learning and mathematical modeling to match identities across identity providers, cloud infrastructure, corporate networks and endpoints.
Rig says internal testing puts RICE’s identity-resolution accuracy above 96%. That figure comes from the company’s own testing and has not been independently verified.
Those connections feed an Identity Dependencies Graph that maps relationships among people, machines, AI agents, accounts, permissions, and active sessions.
Rig then adds an endpoint sensor that observes activity at the device level. The software distinguishes an AI agent’s session from the employee’s own activity and enforces policies against the agent without shutting down the person’s access.
That distinction could become increasingly relevant as companies give AI agents permission to write code, investigate incidents, query internal systems and automate business processes.
Rig says its software is already running inside Fortune 200 companies across financial services, insurance, healthcare and technology. The company has grown to 20 employees and says its platform processes tens of millions of identity activities.
The startup is entering a cybersecurity market that has spent years protecting human and machine identities. AI agents add a third actor that doesn’t always come with a clean identity boundary.
The question for enterprises may soon shift from simply asking who has access to a system to asking something harder: **what is acting through that access right now?**