Extrordinas raises $1.5M to help companies fight cyberattacks with AI-powered incident response
 Nickie Louise
Posted On November 19, 2026
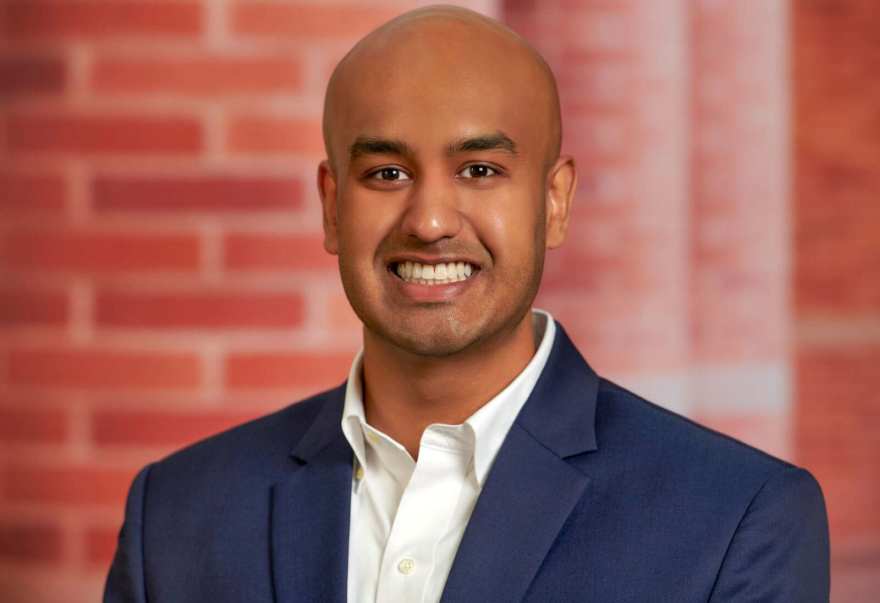
A former CrowdStrike incident response director and a former FBI special agent have teamed up to tackle one of cybersecurity’s toughest problems: helping businesses figure out what happened during a cyberattack and get back to work. Their startup, Extrordinas, has raised $1.5 million from angel investors to build a platform that handles cyber incident response from the first sign of trouble through investigation and recovery.
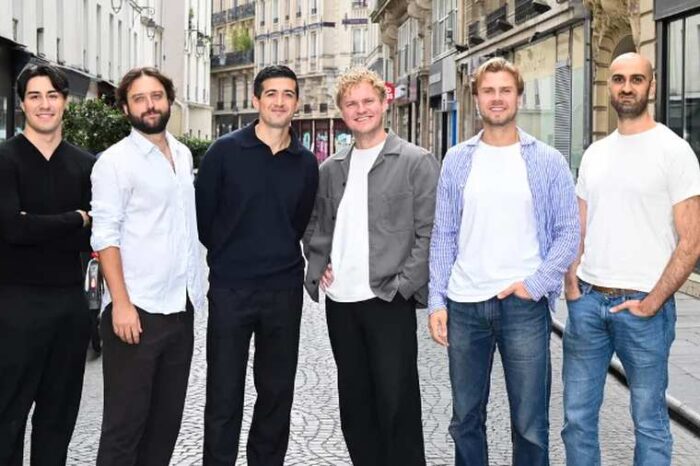
The El Segundo, California-based cybersecurity startup was founded in August 2025 by Jai Musunuri, a former Director of Incident Response at CrowdStrike, and Clark Harshbarger, a former FBI special agent. Musunuri serves as CEO, with Harshbarger overseeing business operations as Chief Business Officer.
The funding comes as artificial intelligence is changing how cyberattacks are carried out. AI tools can help attackers operate at greater scale, placing additional pressure on security teams to investigate incidents and make decisions faster.
Extrordinas is betting that organizations need more than another tool that analyzes security alerts. Its platform brings data collection, threat investigation, and incident reporting into a single workflow, giving security teams a clearer picture of an attack without piecing together findings from separate systems.
The platform addresses ransomware, business email compromise (BEC), insider threats, and attacks involving cloud infrastructure and compromised identities. It uses one-click data collection and proprietary investigation techniques to help identify suspicious activity and determine what happened.
Building a cybersecurity platform around real-world incident response
What makes Extrordinas interesting is the experience behind the product. Musunuri spent years responding to cyber incidents at CrowdStrike, and Harshbarger brings a law enforcement background from the FBI. The founders are applying that experience to software built for incident response firms, managed service providers (MSPs), managed security service providers (MSSPs), and enterprise security teams.
The company uses large language models and agentic AI to assist with analysis, but AI isn’t the entire product. Extrordinas says its approach combines automation with investigation methods and lessons learned from real cyber incidents.
“AI and LLMs are making it easier for attackers to scale, and we’re seeing cyber incidents and attacks increase as a result,” said Jai Musunuri, co-founder and CEO of Extrordinas and a former CrowdStrike Director of Incident Response. “What’s needed is not another analysis tool. It’s a platform that can run incident response end-to-end, with the domain knowledge and edge cases that only come from years of doing this work.”
The distinction matters. Detecting suspicious behavior is one part of responding to an attack. Security teams still need to establish what systems were affected, determine how an attacker gained access, assess the damage, and communicate findings to business leaders. Each additional handoff can slow down the process.
Extrordinas wants to reduce those delays by connecting investigation and reporting.
One customer, Cinch I.T., says the platform has helped its team move faster during investigations.
“Our clients count on us to have answers the moment something looks suspicious,” said Jack Wilson, CEO of Cinch I.T., one of the nation’s fastest-growing managed service providers. “With Extrordinas, we collect the data in one click, see exactly what happened, and give our clients clear answers in minutes, so they can get back to business.”
That customer account offers an early indication of how the software is being used, though Extrordinas has not disclosed broader performance benchmarks, customer numbers, or revenue figures.
The company plans to use its $1.5 million in fresh funding for product development and to expand its sales and marketing efforts. It has not disclosed the individual angel investors participating in the round.
For Extrordinas, the opportunity is straightforward: cybersecurity teams already have tools that tell them something might be wrong. The startup wants to help them determine what happened, what to do next, and how to get the business operating again.